The Geniez AI Framework patented security architecture includes the industry’s most extensive AI guardrails, security controls and governance capabilities
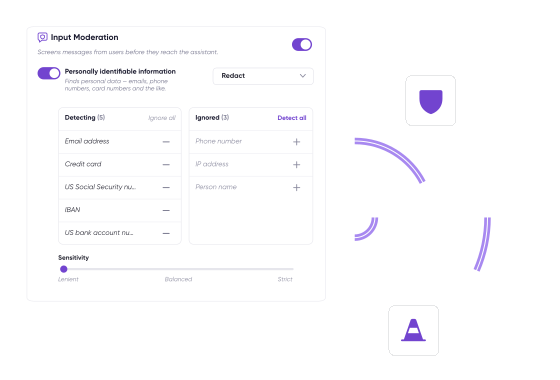

Access is enforced through your existing RACF, ACF2 or Top Secret permissions

Patented access technology ensures users can never do more through the framework than they could in other native interfaces

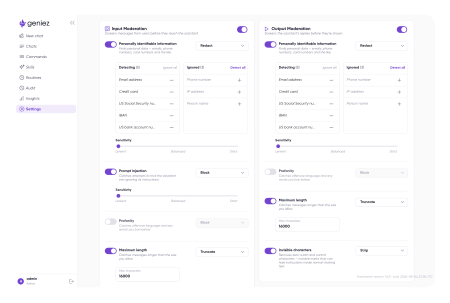
Built-in content modetaion and PII filtering for input and output

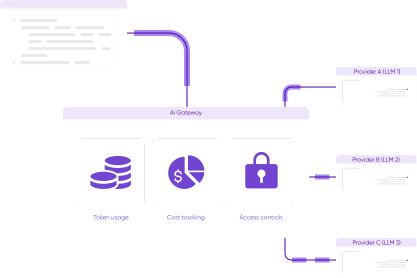
Works with any LLM your organisation chooses, integrating with your existing AI gateway, proxy and unique AI provider requirements

All data remains on-premises and is never shared with the LLM in the cloud
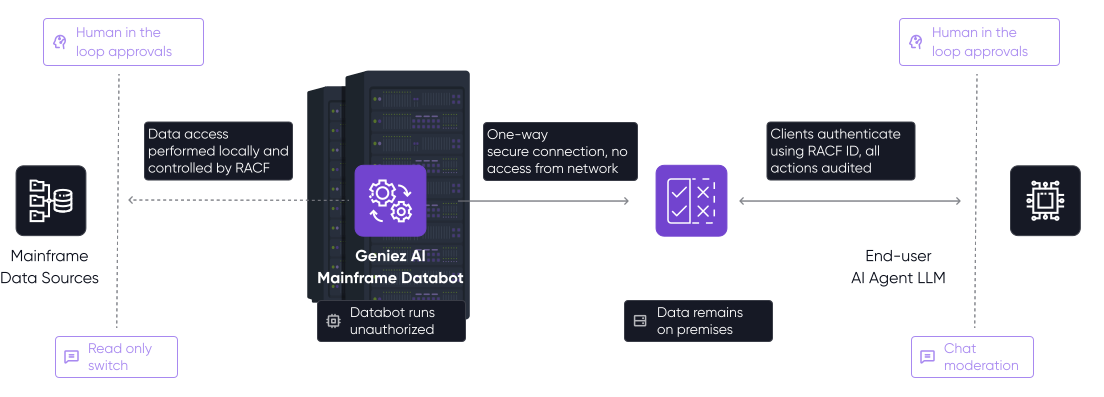
The Geniez AI Framework includes configurable content checks on both input and output, letting clients redact sensitive information or block messages entirely based on adjustable sensitivity thresholds. Paired with a Moderation Judge on user input, filtering stays non-disruptive to genuine tasks.
This is the first line of defense, not the only one. Most organisations already run a consolidated AI gateway managing content moderation across all AI access, and Geniez AI has deep experience integrating with these gateways and proxies. We encourage mainframe teams to connect with their internal AI teams first, so implementations build on existing capability rather than duplicating it.
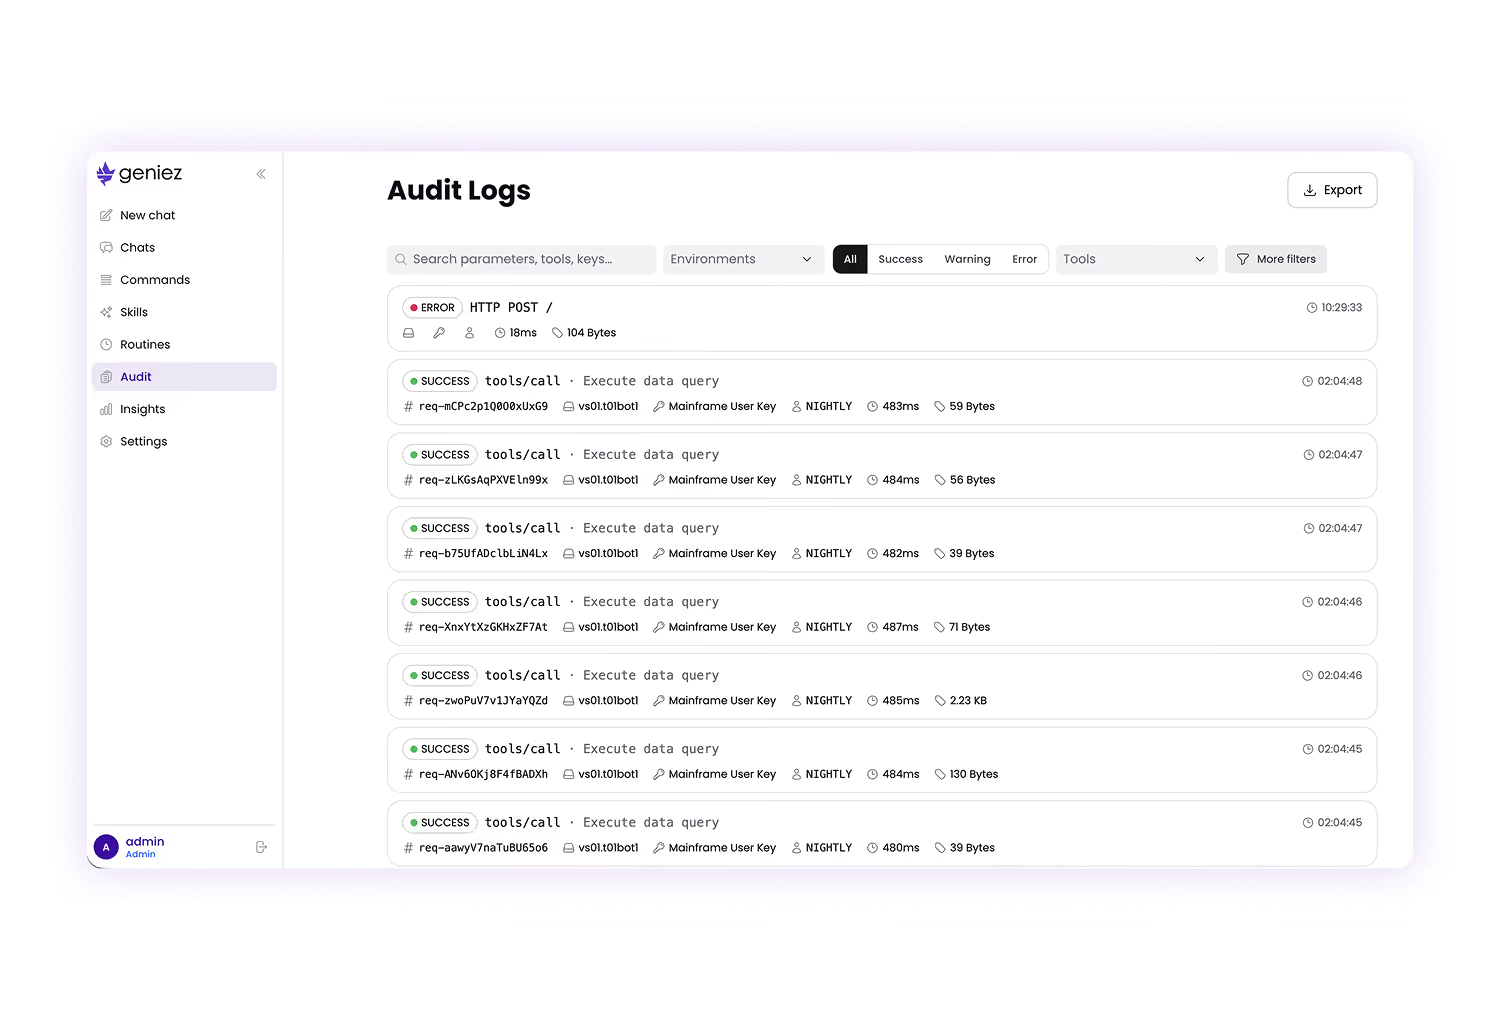
Auditability is a first-class feature rather than an afterthought. Every action the framework takes is recorded and surfaced on a dedicated audit page, giving administrators a single, chronological view of who did what, when, and against which resource. Alongside this, the framework maintains the full chat history for every conversation, so the complete context of an interaction, including the prompts issued and the responses returned, remains available for later review. Both chats and audit records can be exported, allowing organisations to retain them in their own archives, feed them into an existing SIEM or GRC tooling, and satisfy internal review, regulatory examination, or evidentiary requests on demand.
The Geniez AI Framework is built to present the smallest possible attack surface on the mainframe host. All network traffic is strictly one-way, outbound from the mainframe so nothing external can open a session inward or new ingress path for an attacker to probe. Nothing in the framework runs APF-authorized, so it holds no privileged supervisor-state capability and cannot bypass or alter z/OS's own integrity controls, and no component runs with UID 0, so it carries no superuser authority in Unix System Services. In practice the framework operates entirely as an ordinary, unprivileged, outbound-only workload under full RACF controls.

User access enforced through your existing RACF, ACF2, or Top Secret permissions.
Users can never see or do more through Geniez than they can in a standard 3270 session.
Configurable content checks on both what goes in and what comes back.
Every input and output are scanned to ensure no PII data is ever exposed
Tune moderation thresholds to your needs, kept non-disruptive by the Moderation Judge.
Works with your existing AI gateway for moderation, model access, and token tracking.
Use any LLM your organisation chooses, with no vendor lock-in.
Every user authenticates with their RACF ID, and every action is audited.





We don't. The relationship with your LLM provider stays yours, usually managed centrally by your AI team where usage is already tracked. A typical 20k-token conversation usually costs just a few cents, and you can track or throttle usage by provider, model, or user through your existing gateway.
No. Data access is performed locally and controlled by your existing security, and your data is never used to train external models. The connection to mainframe data sources is one-way and secure, with no access from the network side.
Yes. Users authenticate with their RACF ID (ACF2, TopSecret) and all actions are audited, so you retain a complete, attributable record consistent with the controls and processes you already run.